Find vulnerabilities, prove their impact and work with the people who can fix them. That work shapes Pwnry. Franz Bettag combines first-hand security research with experience building and operating production systems.
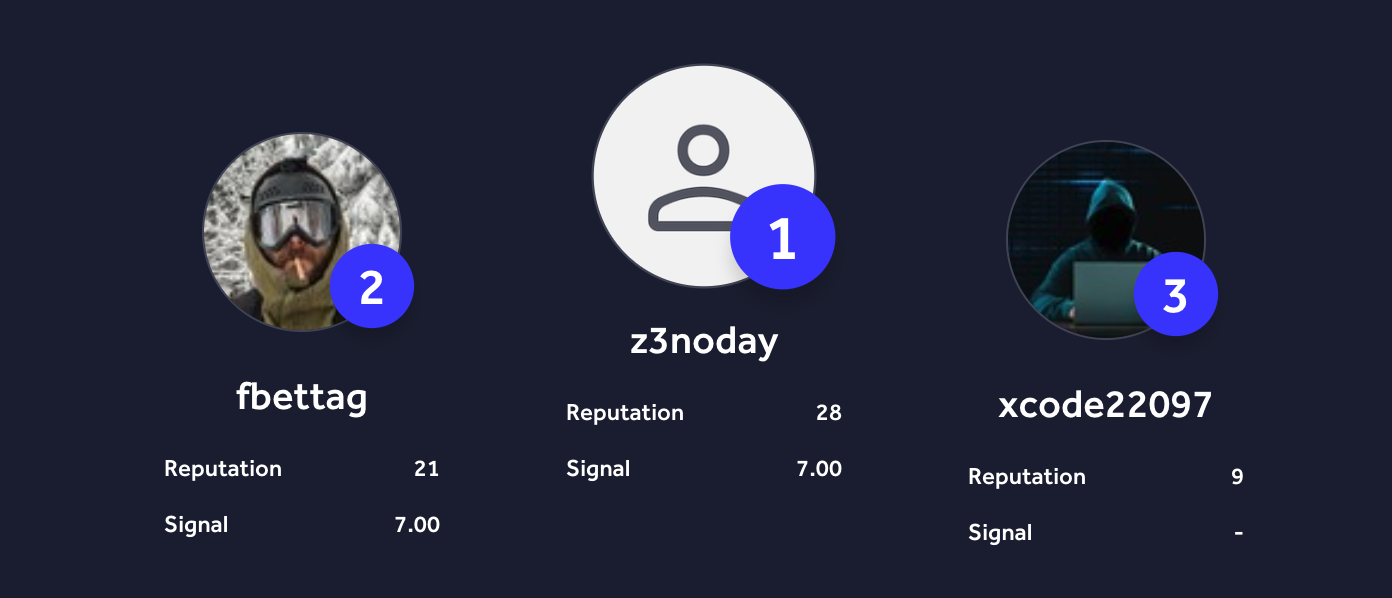
Ranking screenshot from the talk on 16 April 2026. The event listing identifies the ranking as Germany, January to March 2026.
Second place. With a clear context.
The ranking belongs to Franz Bettag in HackerOne’s German VDP category for Q1 2026. VDP means Vulnerability Disclosure Program: a program for responsibly reporting security vulnerabilities. The public event listing and preserved screenshot document that historical standing.
For your pentest, the value is how that experience is applied: a clear testing scope, reproducible evidence and an assessment of real impact.
Published findings. Public fixes.
Documented security research by Franz Bettag, with original sources. Each finding retains its specific credit and fix status.
An out-of-bounds read while processing crafted web content could disclose process memory. Apple published the fix with Safari 27.2 on 26 October 2026 and credits Franz Bettag alongside other researchers.
fasthttp1 publicly documented finding
Request smuggling and mixed responses
PR #2470 · 2026-10-12 · Fix merged
A mismatch between Content-Length and the request body could enable request smuggling and access to other callers’ responses through a shared PipelineClient. The merged fix validates framing, and the pull request credits Franz Bettag for the report.
Keycloak1 publicly documented finding
SAML response validity
CVE-2026-1190 · Keycloak 26.5.4 · Fix published
SAML brokering did not validate NotOnOrAfter in SubjectConfirmationData, allowing SAML responses to remain valid longer than intended. Red Hat rates the issue as low severity and credits Franz Bettag of Bettag Systems for reporting it.
OpenBSD7 publicly documented findings
ldapd: authentication on the wrong connection
CVE-2026-103547 · 7.9 errata 021 · Fix published
An authentication result could be applied to the wrong transaction. OpenBSD published a security fix on 14 September 2026. The upstream commit credits Franz Bettag of Bettag Systems for the report.
isakmpd: short IKEv1 HASH heap overflow
7.9 errata 031 · CVS 1.117 · Fix published
A short IKEv1 HASH could trigger a heap overflow. The public revision documents the fix and research credit for Franz Bettag / Bettag Systems.
isakmpd: privileged monitor file access
CVS monitor.c 1.85 · Public source-code fix
The privileged monitor accepted file paths outside its intended scope. The public change identifies Franz Bettag’s report and patch as the starting point for the repair.
isakmpd: policy path traversal
CVS policy.c 1.107 · Public source-code fix
Policy paths derived from peer data could traverse directories. The public source history documents the repair in connection with Franz Bettag’s research.
npppd: path validation across the privilege boundary
CVS HEAD privsep.c 1.31 · Fixed in HEAD
A worker could request file opens without sufficient path validation. The public change credits Franz Bettag for the finding and initial patch.
npppd: stack bytes in an IPCP reply
CVS HEAD ipcp.c 1.7 · Fixed in HEAD
An oversized IPCP request could expose stack bytes in a ConfRej reply. The source history credits Franz Bettag for the report and initial patch.
npppd: PPPoE TLV length handling
CVS HEAD pppoed.c 1.27 · Fixed in HEAD
PPPoE TLV length handling could access memory out of bounds. The public change credits Franz Bettag for the report and fix.
NetBSD1 publicly documented finding
IPsec: mbuf overrun
kern/60669 · HEAD fix · Fixed in HEAD
IPV6_IPSEC_POLICY could overrun an mbuf. The public report names Franz Bettag as the person who forwarded the issue. It is fixed in HEAD; the report remains needs-pullups, with release-branch backports pending.
Takeovers and other talk cases.
Publicly described in the talk on 16 April 2026. These cases are attributed to the speaker’s own documentation, with direct links to the relevant slide.
Opera
1 documented case
A subdomain takeover involving SIP/VoIP infrastructure. The talk describes dangling SRV references, a manually confirmed takeover and responsible disclosure through Bugcrowd.
Bring research, engineering and operations together.
Franz Bettag develops and operates his own platform for AI-assisted security research. The work combines specialized testing steps, fresh reproduction and technical documentation, alongside his experience with production Unix, Go, Elixir and Kubernetes systems.
For Pwnry, that sets a practical standard: assess automated signals, substantiate findings and make remediation actionable for your engineering and operations teams.
How should I interpret the report and finding counts?+
The el8 archive lists 10 platform reports marked resolved and 11 findings with public fixes. The sets may overlap. HEAD fixes are identified on each entry; NetBSD release backports remain pending. Talk cases are listed separately with their own source.
What exactly does the #2 ranking mean?+
It is Franz Bettag’s historical standing in HackerOne’s German VDP category for January to March 2026. The public event listing and original screenshot document the period and category.
How does this research help my pentest?+
It brings experience with attack paths, practical reproduction and expert impact assessment. In a contracted pentest, we translate that into substantiated findings and concrete remediation steps.
Where can I check the evidence?+
Pwnry preserves the historical ranking screenshot and links to the event listing. Published research findings link directly to vendor advisories, CVE records and the upstream commit with credit.
Have your own attack surface checked.
Start with the free company check. We agree the full pentest and its scope together.